Every digital system has a security layer. Your life has no one of its own.
Status: public draft · the long version — prior art, the full map of interactions, requirements and sources — is being prepared at /security-model/review · the map — how this side connects to the world: /world
In short
Security already runs the digital world. But who is protecting your life?
Your phone protects itself. Your bank protects the money. The AI company protects the model. None of them holds your side — the one place where all of it lands: your time, your money, your attention, your decisions, your next step.
You would never give every shop the password to your bank account so it could decide what is right for you. The shop asks your bank for one decision. It does not receive the account behind it. We think the rest of your digital life needs the same boundary.
We are building a human operating system, and we think its security model has to be written for the person, not borrowed from the systems around them. This page says why, what that model is, and — as honestly as we can — how much of it exists today.
Security already decides what everyone is allowed to do
Some forms of abuse are rare relative to legitimate use. Stripe sees fraud in roughly one payment in a thousand — and checks more than a thousand characteristics of every payment in under a hundred milliseconds to find it, blocking about 0.1 per cent of legitimate payments by mistake along the way (Stripe). About 6.2 per cent of the web traffic Cloudflare carried in 2025 was mitigated as potentially malicious or blocked by customer-defined rules, 3.3 per cent of it as DDoS attacks or by managed rules (Cloudflare Radar, 2025 Year in Review).
That is the first thing to understand about security: a small fraction of abuse redesigns the experience for everyone. Much of the friction you touch today — passwords, one-time codes, CAPTCHAs, confirmations — exists because of that fraction. We are not complaining. It is proof of how seriously the world takes the protection of systems. We are asking why that seriousness stops at the edge of each system — and so rarely reaches the person standing on the other side of it.
Two waves, one pattern
Cards. When payment cards spread, thieves took the card itself. As chip adoption made counterfeit card fraud much harder — down 87 per cent at chip-enabled US merchants (Visa) — criminals kept adapting. Today a payment can be fully authenticated and still be the result of manipulation. In the United Kingdom in 2025, banks prevented £1.68 billion of unauthorised fraud — and in the same year people lost £576 million by authorising payments themselves, after someone had convinced them to. 248,070 cases, up seven per cent; two thirds began online (UK Finance, 2026).
The payment can be authenticated. The cryptography can work. The person can still lose.
Agents. Now software does not only know. It acts: buys, books, applies, negotiates, moves money. In 2025 pilot tests of a browser agent, hidden instructions on a web page hijacked it 23.6 per cent of the time before mitigations and 11.2 per cent after (Anthropic, 2025); the product has since gained further action-level safeguards. An agent can be talked into acting against you the way a person can. The payment industry is answering with signed mandates (AP2): AP2 lets verifiers cryptographically check that a checkout and a payment match the mandate you signed, shares only the relevant constraints of that mandate, and returns receipts. That is the right answer to its question. Our question begins one level above: does that mandate still fit the rest of your life now?
Each wave shows the same limit: securing the transaction or the agent does not automatically secure the human outcome. Whatever passes through the technical layer lands in a person's life. How long do we keep doing this — securing every new system separately, and leaving the person to carry what is left?
Not every loss looks like fraud
Adults in the United Kingdom spend four and a half hours a day online outside work; 18-to-24-year-olds, six hours twenty minutes; most of it on a smartphone, across 41 apps a month (Ofcom, Online Nation 2025). Time itself is not harm. But in July 2026 the European Commission preliminarily found the addictive design of Instagram and Facebook — infinite scroll, autoplay, push notifications, highly personalised recommendations — in breach of the Digital Services Act, citing risks to the physical and mental wellbeing of users, including minors and vulnerable adults (European Commission, 10 July 2026); TikTok received the same preliminary finding in February. These are preliminary findings, not final decisions. But read what the Commission said, in its preliminary findings on TikTok, about the tools that already exist: the screen-time tools are easy to dismiss and introduce little friction, and the parental controls require additional time and skills from parents. The protection was there. It was left to the person to operate. The point stands: the problem has become large enough that governments are changing the architecture of access itself. Law can set a floor for millions of people. It cannot carry one person's changing limits from one service to the next.
Sometimes what disappears is money. Sometimes it is an hour, a decision, a night's sleep, or a goal you did not choose.
Every system meets you separately
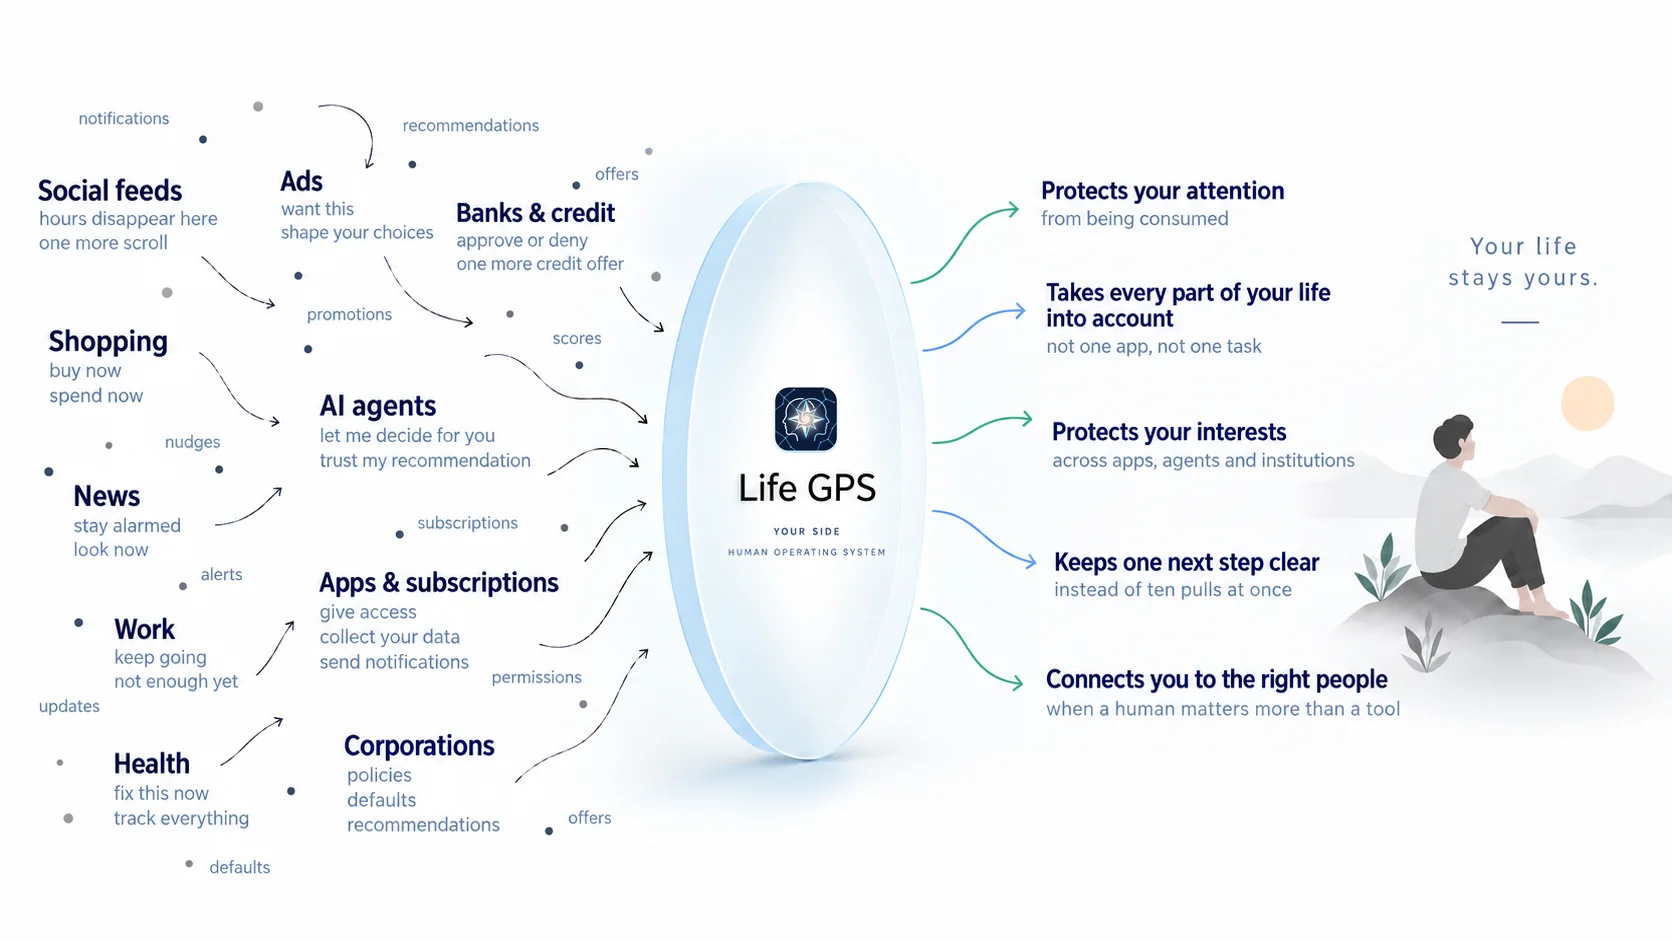
Forty-one apps. Many build their own model of you; each holds its own settings, asks its own permissions, sends its own notifications — and sees its own part. Between them, you are the integration layer.
Remember the bank. It keeps the account on its side. The shop asks for a transaction. It receives a decision — not the account.
Why should the rest of your life work differently? Why should a digital service need every part of your life to answer one question?
What is missing
Not another lock. Today you carry the connections in your head.
Your bank knows your money, but not what you promised your family. Your work agent knows the deadline, but not what your health can take this month. A shop knows the purchase, but not what else that money was meant for. A feed knows what keeps you watching, but not what you wanted this evening for. Each of them can be right on its own — while your life loses in the sum.
What is missing is one side that stays with you across all of them: it knows your limits, your priorities and your direction, and answers for you when a shop, a bank, an employer, a feed or an agent asks for something. A payment mandate asks: did you authorise this purchase? The question above it: does this purchase still fit your life today? The mandate can be valid and the purchase can still be wrong for the person.
For researchers and builders: two layers are already being engineered well — what may you know about me? (credentials, consent, minimal disclosure) and what may you do for me? (permissions, scopes, signed mandates), with mediation layers now emerging between agents. The third question sits above them: what remains acceptable for this person, across every part of their life, right now? Among the systems we reviewed, we have not found one independent person-side layer that combines, across many executors and over time, constraints across the person's life, arbitration between domains, minimal disclosure, protection from reconstruction, where goals came from, protection that continues after an authorised action, and consequences returned into one changing life. If you know prior work that does this, tell us. Who holds which piece today — states, mandates for one part of a life, guardians, and the groups building the technical layers — is drawn on one page: the map of the person's side. The full comparison goes to /security-model/review.
FROM THE FOUNDER → Start from the person — Protection of the person has to become technology too. Why I am building it.
What we are building
Life GPS is a human operating system. Security is its kernel.
Security is not a feature of Life GPS. It is the condition that makes Life GPS possible. A human operating system needs its own security architecture. Not the model's. Not the bank's. Not the platform's. The person's.
In plain language: protection is designed into the operating system of your life, not added after something goes wrong. And it is not about adding more security work to your life. It is about taking security work out of it. Less explaining yourself. Less managing permissions. Less checking whether every new tool is pulling a different part of your life in a different direction. You live. The operating system does the coordination.
The protected thing is not only your data. It is your identity, money, time, attention, relationships, goals, authority and continuity. The threat is not only a hacker. It can be a scammer, an over-permissioned agent, a manipulative interface, a wrong inference, a compromised provider — or the protecting system itself becoming too powerful.
Models are capabilities. Agents are executors. The person has their own side.
Access to a tool is not permission for every action: a real case from the founder's work with an autonomous agent.
One person. One side. Many executors.
The system does not decide what a good life is for you. You define the boundaries; it remembers them, shows conflicts, asks again when the context changes — and the final decision stays yours. The same boundary applies to Life GPS itself. Our own recommendation does not get a free pass.
Security holds the boundary. The Protocol carries your rules into interactions with the outside world. Human Antivirus keeps checking whether even an authorised interaction is still working for you. Recovery keeps your side yours when a device, a model or a provider fails.
We do not need to replace the bank, the shop, the model or the agent. We need each of them to meet the person's side. The better the executors become, the more important an independent side of the person becomes.
Every agent can be right about its task while the combined result is wrong for the person. A financial agent sees money. A work agent sees work. A health service sees health. The person has one life. No executor should optimise one part of your life by silently spending another. That is why the person's side has to see across every part of the life — and why no other executor needs to hold all of it.
You establish your side once, and it evolves as your life changes: money · time · attention · privacy · what needs your confirmation · what may never be given away · the constraints of your health, your family, your work, your faith, your risk. Then every connected executor — an agent, a shop, a bank, a model — comes to that side and asks what it may do. It receives a decision: allowed · adjust · needs your confirmation · not allowed · not enough context. It gets the decision it needs, not the life that produced it.
An agent should be like an app inside an operating system: powerful, useful, replaceable — but it does not decide its own permissions. On a phone, an app's capabilities are set from outside the app, and stay limited even if the app is compromised (Apple, App Sandbox). We are building that boundary for the person. From blockchain we take trust minimisation, verifiability and resistance to unilateral control — and leave the public ledger of your life behind.
Across money, health, work, attention, relationships, institutions and AI, the pattern is the same. Each outside system sees a part. Your side carries the limits and priorities you set, shows the conflicts between them, and gives each interaction only what it needs. The final decision stays yours. That is the target architecture; the honest status of each part is below.
What a human operating system has to protect — all of it
If we claim to hold every part of a life, we do not get to choose only the easy parts of security. Twenty-six areas, as six questions a person would actually ask. The technical name is there for the engineers; the status comes from the code, not from the ambition, and is explained in Where this stands today and on /security-model/review.
Who are you?
- You can change without losing continuity — identity & continuity ·
NOT YET - Permissions end and can be taken back — time & revocation ·
NOT YET - One breach does not own your future — post-compromise security ·
NOT YET - Lose a device or a provider, not yourself — recovery ·
PARTIAL - Children are not treated like adults — children & guardians ·
PARTIAL
What can leave you?
- Share the answer, not everything behind it — data & disclosure ·
PARTIAL - An answer cannot silently become a new permission — information flow ·
NOT YET - Separate pieces should not rebuild you — correlation & reconstruction ·
NOT YET - Keep computation on your side where possible — where computation happens ·
PARTIAL - The cryptography can change without losing you — cryptographic layer ·
NOT YET
Who can act for you?
- One task. Minimum power. Clear limits. — authority & delegation ·
NOT YET - No blind trust — including us — trust & separation of powers ·
PRINCIPLE - Protection rules cannot quietly weaken — policy integrity ·
NOT YET - Important actions leave a readable trace — audit & receipts ·
NOT YET
Who can influence you?
- Your goals stay yours — goal integrity ·
NOT YET - Fact, claim and AI inference stay separate — memory integrity ·
PARTIAL - Your attention is not inventory — attention & manipulation ·
LIVE IN PART - Life GPS is inside its own threat model — protection from the system itself ·
PARTIAL - One part of life cannot silently spend another — cross-domain consequences ·
LIVE INSIDE LIFE GPS - Other people remain separate people — relationships & other people ·
PARTIAL
What if something fails?
- Outside content cannot give itself authority — untrusted content & injection ·
PARTIAL - One breach has a ceiling — compromise containment ·
NOT YET - A locked device and an unlocked one are different risks — device & OS layer ·
NOT YET - Keys, logs, access and secrets matter too — infrastructure & operations ·
LIVE - In a crisis, protection comes first — crisis & safety ·
LIVE
Who protects you from the protector?
- Consent is not consent if surrender is the price of basic access — legal alignment & coercion ·
PRINCIPLE
Across all twenty-six: human verification — the people who know you notice a substitution · security is not for sale — no advertising, no business model on the person's data · measurement and honesty — answers at scale, failures published, independent audit.
Those twenty-six lines are what has to be protected. This is where that protection has to follow you:
Money · Shopping · Health · Work · Government · Education · Media & attention · AI & agents · People & relationships · Home & mobility · Faith & values · Crisis & safety. Different parts of life. One person. One side.
For businesses, and for the people who build agents
You should not need to know every part of a person's life to serve one part of it. A shop needs to know whether this purchase can proceed. A bank needs the confirmations the loan requires. An agent needs to know what it may do. Life GPS keeps the rest on the person's side — and you do not have to know more about a person to serve them better. Ask the person's side what you need for this interaction. Get the answer, the mandate or the confirmation — not the life that produced it.
Concretely, that is not give me the profile. It is four questions and a receipt: can this action proceed under this person's current mandate? what minimum confirmation is required? what minimum disclosure is sufficient? what constraints must this service respect? — and, when it is done, an outcome receipt back to the person's side. That can mean less sensitive data on your servers, less guessing, and potentially fewer wrong actions, returns and disputes. You keep your business; you connect to the person through the protocol.
The API we are designing is access to the person's boundary, not access to the person's database.
For builders. MCP gives models a common way to reach tools and capabilities. Think of Life GPS as working on the other side of that interaction: the persistent person-side policy and context those capabilities have to meet. MCP asks what tool can I call? The human operating system asks what may this tool know, do or spend for this person right now? An analogy, not the same protocol — what matters here is whose boundary governs the interaction.
Establish it once. Carry it everywhere.
This is not twenty more confirmations. Security engineers have a name for the opposite: secure by design — the complexity of security configuration should not be the customer's problem, and the burden should not fall on the person alone (CISA). You should not have to become a security expert to keep your own life yours.
Nor is your side a rulebook written once and forgotten. Establish it once. Let it evolve continuously. Ask again when the consequence changes. That is why this takes context across the person's life, a running check on outcomes and a human antivirus — not a settings screen. That is the target. We describe it as a target, not as a finished product.
Where this stands today
The architecture is designed so that the richest context stays on the person's side and outside systems receive purpose-sized answers instead of everything about the person. Some parts of that boundary are already implemented; some are still being closed, and we publish the gaps.
What exists. Between the model of the person and any external AI model there are checks on what may be sent; the person's memory, the saved picture of their life, the context of their route and their contacts are excluded from it by construction; the model provider is a replaceable component. A boundary for untrusted content and a detector for injected instructions exist. Crisis handling works offline (Life GPS is not a medical, emergency or crisis service — it points to real help). The constraints that govern the system are published. published. Scoring a person with a number is forbidden by a law of the system.
What does not exist yet. Not every part of the exchange with an external model is reduced to the same standard yet — closing this gap is open work. Some protective controls are still moving from testing to actively blocking harmful actions. There is no separately verifiable protective component; parts of it exist. The production recovery layer — coming back to your own life on a new device without a permanently reconstructable identity — is a requirement of the architecture and is not complete. Connections to institutions and agents through the protocol are not switched on. Live calls between people are built and not switched on. There has been no independent audit. Our /security page says we do not claim our systems are secure. That line stays.
The direction is not ours alone. Identity standards already recommend giving a service a derived answer — over 18: yes — instead of the date of birth, wherever the derived answer is enough (NIST SP 800-63C-4). Our next step is to apply that principle not to one credential but to the interactions of a life over time. The outside world does not need the life that produced the answer.
People, not profiles
Someone has a problem. Someone else has the relevant experience. The match does not require either side to hand over an entire profile — only enough to establish that the need and the capability fit. They talk, help, and return to their lives.
That is a design principle, not a live feature: calls between people are built and open with the first round. We put it here because it shows what the architecture is for. Data is not the product. The value is the right interaction with the minimum disclosure.
What the first round is for
Not a roadmap. The first round turns architectural constraints into a system that can be measured under real use: recovery in the released product, blocking harmful actions rather than only recording them, independent checks of encryption, and protection against piecing together a person's private life as exchange with institutions opens, independent red teams and audit.
Some answers only exist at scale: how much context stays on the person's side in practice; how often protection fires wrongly; the minimum authority an agent needs; how fast revocation propagates; how reliably a person's continuity can be restored after loss or compromise; whether separate disclosures can be joined; whether the protection itself starts to push the person. We do not promise the result. We promise the measurement — and to publish it, including where the architecture fails.
Why any of this
Protection is not the point. The point is what it gives back: not explaining yourself to every service; not spending your life in consent screens and settings; agents doing the routine without governing your direction; your money, your time and your attention not spent by every optimiser separately; people and services arriving when they are needed — and the rest of your time staying yours.
We spent decades building layers to protect transactions, devices, accounts, networks and models. The next layer is teaching the digital world how to work with a person without taking the person apart.
When your side belongs to you, technology can finally do more without taking more of your life.
The model can change. The agent can change. The service can change. Your life stays yours.
Do not believe us. Break it: /security. Prior work we have missed, an error, a sector you want to test with us — hello@lifegpsos.com.